Find and fix issues 10x faster with Red Sift Radar
Integrating internet-scale intelligence, security expertise, and the power of an LLM, Radar empowers defenders with actionable insights to close security gaps before they can be exploited.
Integrating internet-scale intelligence, security expertise, and the power of an LLM, Radar empowers defenders with actionable insights to close security gaps before they can be exploited.






Resolve security issues 10x faster - investigations across emails, domains, and internet-facing assets that used to take 20 minutes can now be completed in just 2.

Utilize LLM-driven insights and Radar’s contextual understanding to receive tailored guidance on your specific issues.

Eliminate manual tasks and data collection by seamlessly integrating deep cybersecurity intelligence into your existing systems.

Translate complex security tasks into simple, natural language conversations, empowering both technical and non-technical users to quickly master advanced troubleshooting.
Start with Radar, your AI companion inside Red Sift, then extend it with in-app agents or your own LLM. However your team works, Radar meets them where they already are.
Radar: your AI security companion
Natural-language conversations. Ask Radar about your email, domains, and internet-facing assets and get clear answers, no deep expertise required.
Contextual fix guidance. Radar understands your setup, so troubleshooting steps are tailored to the exact issue you’re facing.

Radar Agents: AI built into your Red Sift apps
AI source classification. The AI Classifier evaluates DMARC sources against a broader dataset than traditional if/then logic, delivering higher-confidence classification scores.
Account-aware remediation guidance. Get fixes tailored to your specific account data and configurations, not generic advice that might not fit the issue.

Radar MCP: Red Sift in your LLM of choice
Every Red Sift product, one conversation. 52 tool capabilities, accessible from Claude, ChatGPT, Cursor, VS Code, or whatever AI assistant your team already has open.
Read and write actions, not just lookups. Classify a lookalike, add a domain, activate Dynamic SPF, update DMARC tags, and more, without leaving the chat.
Why security teams choose Red Sift Radar
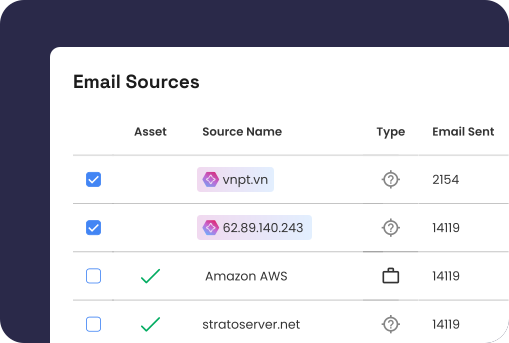
Get a real-time view of your digital estate
Internet-scale cybersecurity intelligence and a global network of monitoring points help you gain real-time visibility into your digital environment.
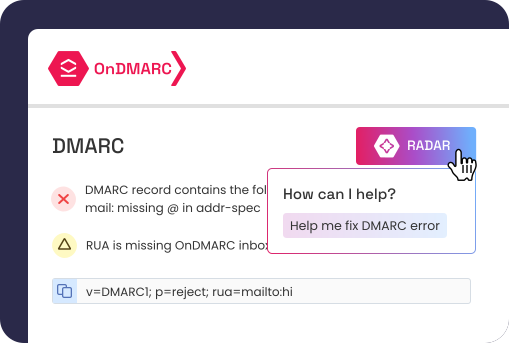
Understand and fix misconfigurations on the fly
Continuous assessment of your assets identifies and notifies you about misconfigurations you didn't know existed. Conversation-based fix guidance makes remediation a breeze.
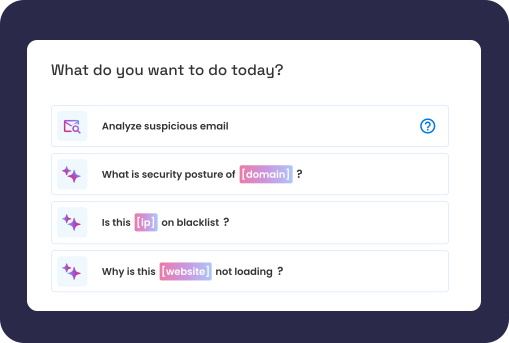
Use AI for preventative defense
Analyze vast amounts of security data to detect exposures, prevent configuration drift, and classify assets or suspicious activity. Provide your users with detailed assessments to support informed, proactive decision-making.
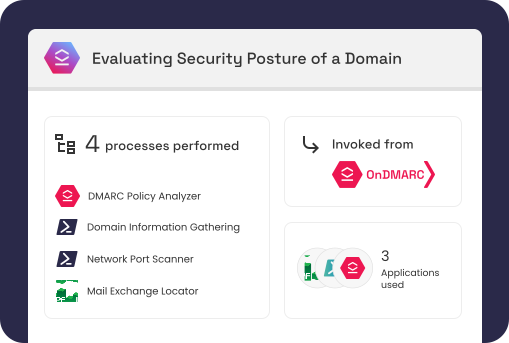
Benefit from consistent, proactive security at scale
Rely on built-in expert playbooks to guide multi-step security analyses with precision, delivering accurate outcomes even in complex scenarios.
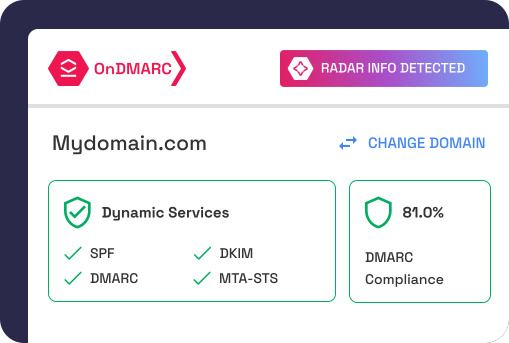
Share clear reports and documentation
Generate detailed reports and explanations of security configurations and issues, giving IT teams and third-party stakeholders the context they need to resolve problems fast.
Integrated across Red Sift, and beyond
Chat with Radar from anywhere across the Red Sift platform, or connect it to the LLM your team already uses with Radar MCP. All of the insights and tools you need where you're already working.
How Radar and OnDMARC strengthen your email setup against phishing and other email-based threats
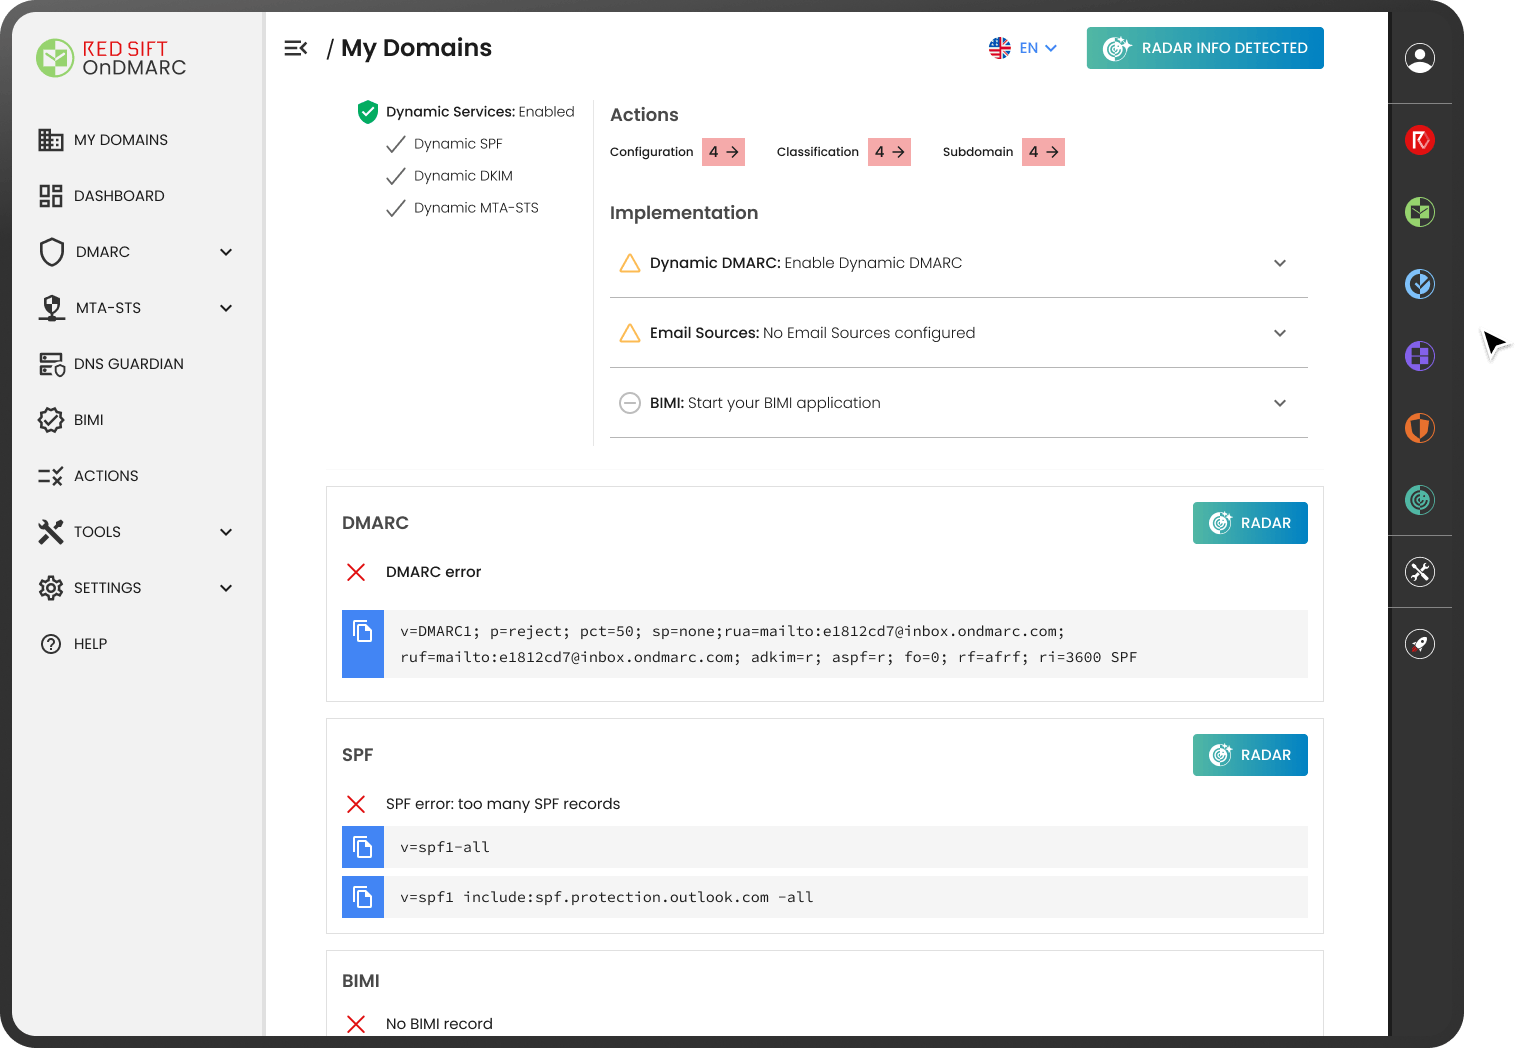
Radar integrates with Red Sift OnDMARC, making it the first LLM embedded in an automated DMARC application. Get real-time answers to specific email-related queries and diagnose misconfigured records or settings in seconds.

“With Radar, [my threat analysis] process has been streamlined, reducing the time to approximately 2 minutes per domain.”

“In the first 24 hours of use, Radar saved us $4,000 by identifying a fraudulent invoice from its header information.”

“Radar gives us a quick and easy way to not only check the configurations, but also to provide IT professionals with excellent documentation and explanations of the problem, along with information to fix the issue.”
“Radar helped me identify an opportunity to tighten security around one of my email domains with an MTA-STS policy. It explained why the policy is important, walked me through the steps to configure and enable it, and even verified that I had everything configured correctly afterward. Incredibly helpful!”
“With Radar, [my threat analysis] process has been streamlined, reducing the time to approximately 2 minutes per domain.”
Red Sift Radar frees up your team and eliminates manual work by combining deep cybersecurity intelligence with real-time AI analysis—through a single workflow.
Gathering insights
Identifying and diagnosing misconfigurations
Troubleshooting complex queries
Tap into a single source of truth to get a real-time view of your security posture, including domains, email, and internet-facing assets.
Auto-detect misconfigurations in SPF, DMARC, and other critical records, providing immediate guidance and resolution.
LLM-driven recommendations help resolve exposures, including syntax issues and email-related exposures.
Use a mix of complex tools like MXToolBox, DNS Toolbox, WHOIS, and Qualys/SSL Labs.
Manually checking domain configurations, email security, and web infrastructure, costing you time.
Rely on forums like Reddit or Stackoverflow and require in-depth terminal/command prompt skills and the ability to read RFCs for manual diagnosis.
Taking action
Ask Radar what’s wrong and how to fix it, classify and verify issues in Red Sift with Radar Agents, or take action straight from your own LLM with Radar MCP.
Log in to several tools, piece together the evidence, and make each change by hand.
Fill out the form and a team member will be in touch to get you set up
FAQs
For Red Sift customers, Radar is included within certain tiers of our products. If you are not yet a customer but would like to see Radar in action, fill out the form on this page and a team member will be in touch.
Red Sift Radar is included with certain tiers of our products. If you are an OnDMARC customer, check out pricing here.
We initially prototyped Red Sift Radar as a plugin running on top of the public version of OpenAI’s GPT-4 but decided to bring the LLM into our platform so we could build a safer and more capable experience.
No, we do not use customer data for training purposes. Data shared in OpenAI interactions is not used to train or improve models.
Ready to see for yourself?