Solve email security and improve deliverability faster with Red Sift OnDMARC
Red Sift OnDMARC defends your brands from attackers by securing your email setup against business email compromise (BEC) and spoofing.


Red Sift OnDMARC defends your brands from attackers by securing your email setup against business email compromise (BEC) and spoofing.






How leading teams approach security is fundamentally changing. The only path forward is to proactively anticipate risk instead of reacting to incidents.

Block phishing and spoofing attempts to eliminate the most common entry points for cyberattacks.

Make sure important messages, such as security alerts and customer communications, consistently reach inboxes.

Stop domain impersonation to safeguard your reputation and maintain customer trust.
Red Sift OnDMARC helps you achieve DMARC enforcement safely and efficiently, putting an end to unauthorized use of your email sending domains.
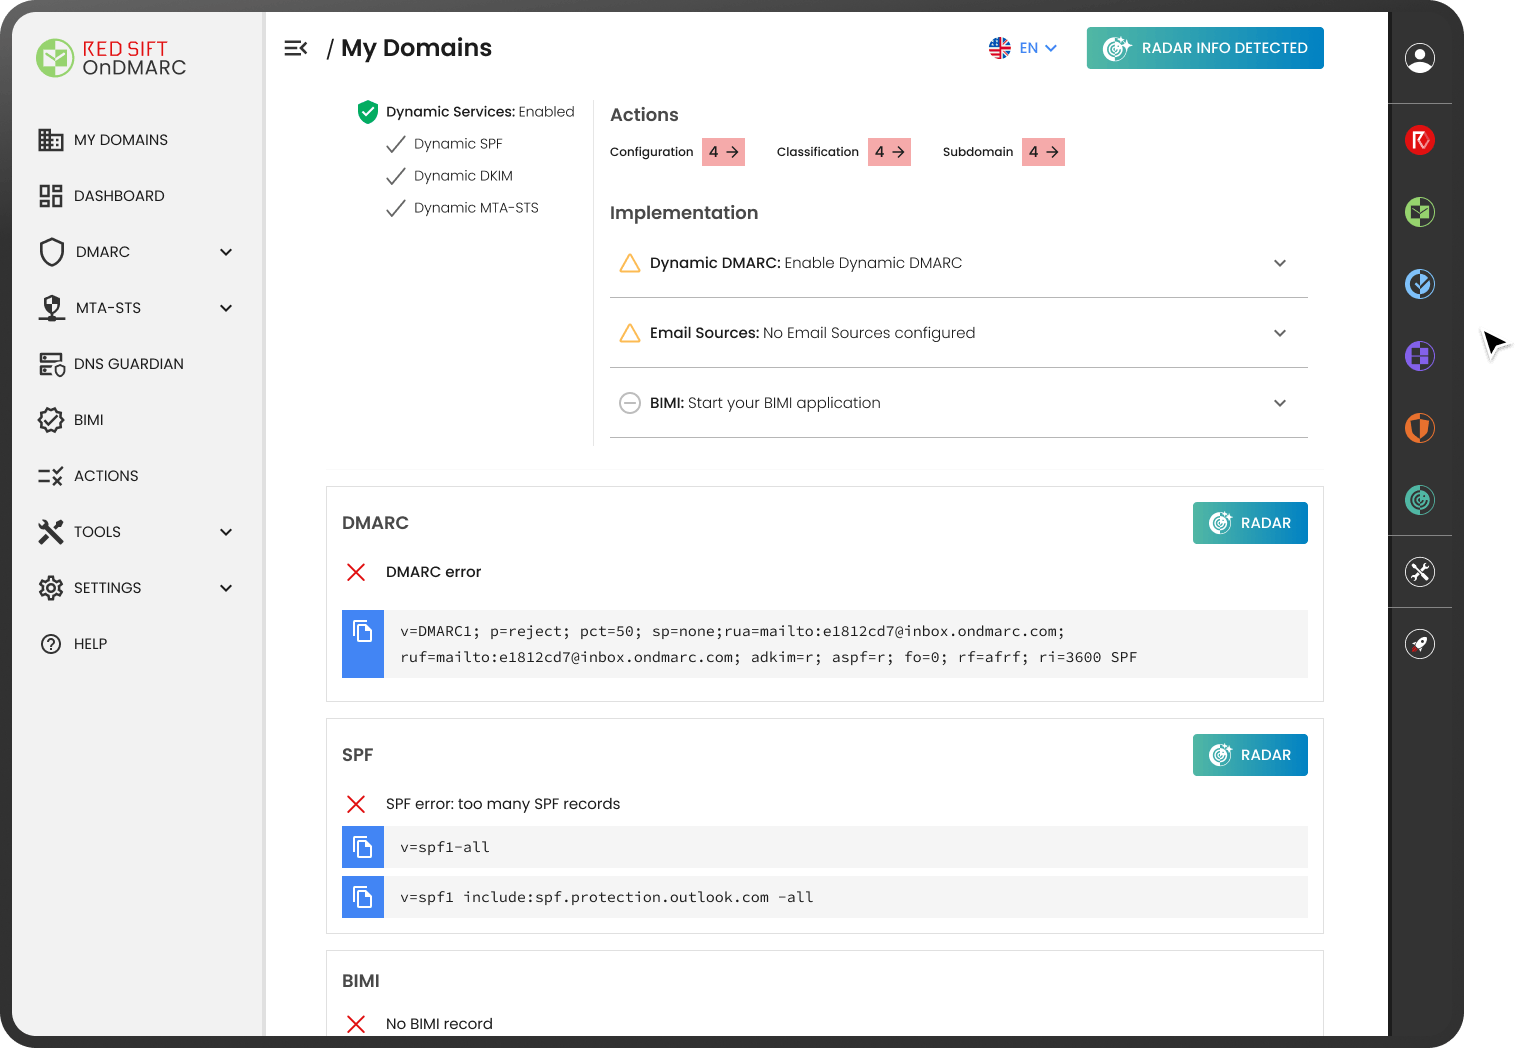
Red Sift Radar is the first LLM directly integrated with Red Sift OnDMARC, providing instant, AI-powered diagnoses of email security issues. It identifies misconfigurations in SPF and DMARC records, uncovers unknown senders, and enhances your understanding of DMARC reports.
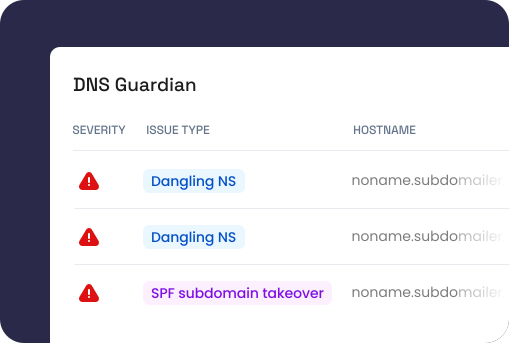
Red Sift OnDMARC is the only DMARC application on the market that can identify and stop malicious mail that bypasses DMARC, including spam from domain takeovers and SubdoMailing.
Red Sift OnDMARC makes the deployment of the MTA-STS protocol fast and simple so you can secure your inbound email and prevent intercepted messages.
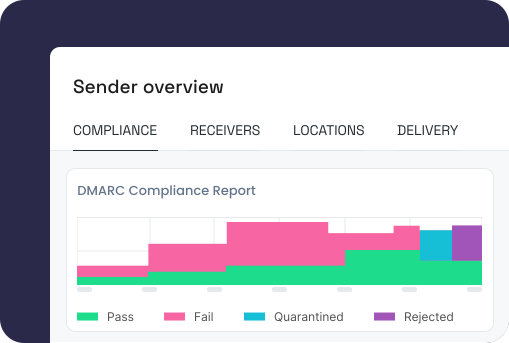
Forensic reporting meets machine learning to deliver granular information about emails that failed DMARC authentication on the receiver side while protecting user privacy.
Red Sift OnDMARC is the only BIMI solution on the market with integrated VMC provisioning. Improve open rates by 39% and increase brand recall by 44%.
Streamline SPF management and avoid manual DNS changes. No macros means that all legacy email structures, gateways, and receivers will deliver your emails.
Make a one-time DNS change and manage all of your email authentication from OnDMARC’s UI. Save time, avoid manual configuration errors and quickly add, authenticate or remove services.
Our customers see a 6-8 week average time to full DMARC enforcement (p=reject or p=quarantine). Our award-winning application helps organizations of all sizes reduce email security risk as efficiently and effectively as possible.
Red Sift Radar frees up your team and eliminates manual work by combining deep cybersecurity intelligence with real-time AI analysis—through a single workflow.
Gathering insights
Identifying and diagnosing misconfigurations
Troubleshooting complex queries
Tap into a single source of truth to get a real-time view of your security posture, including domains, email, and internet-facing assets.
Auto-detect misconfigurations in SPF, DMARC, and other critical records, providing immediate guidance and resolution.
LLM-driven recommendations help resolve exposures, including syntax issues and email-related exposures.
Use a mix of complex tools like MXToolBox, DNS Toolbox, WHOIS, and Qualys/SSL Labs.
Manually checking domain configurations, email security, and web infrastructure, costing you time.
Rely on forums like Reddit or Stackoverflow and require in-depth terminal/command prompt skills and the ability to read RFCs for manual diagnosis.


Streamline your DMARC journey—unlock Red Sift OnDMARC today!